Cybersecurity researchers have uncovered a large-scale SEO poisoning campaign that manipulates search engine results to distribute malware and funnel victims into fraudulent technical support scams.
The campaign, dubbed BengalSEO, has been active since at least 2015 and is believed to operate from India’s Rajasthan state. Researchers at the DFIR Report said the operation is linked to two IT service companies, WeConnect Solutions LLC, formerly known as iConnect Soft Solutions LLC, and Garage2Global.
While Garage2Global presents itself as a provider of website development, SEO and digital marketing services, investigators found evidence suggesting that the company has been involved in building malicious web infrastructure used in BengalSEO’s operations.
How the BengalSEO Campaign Works
BengalSEO combines black-hat SEO techniques, malicious websites and traffic distribution systems (TDS) to attract victims through search engines.
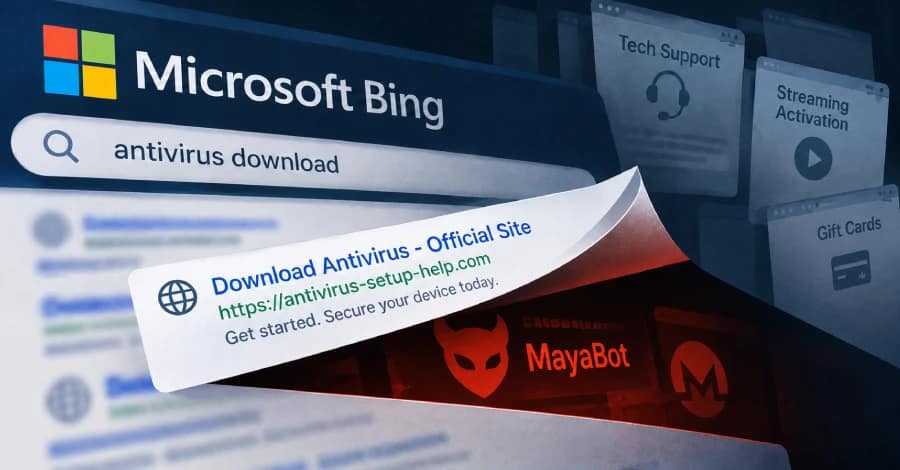
The attackers create fake web pages designed to appear legitimate and then manipulate their search rankings so they appear prominently in results, particularly on Microsoft Bing.
The pages impersonate technical support and service activation websites for popular services. Other lures promote downloads for antivirus products, gaming software and tax-related utilities, while some pages claim to help users activate credit cards, healthcare benefits or gift cards.
According to the DFIR Report, the campaign uses an elaborate redirection infrastructure to determine who visits the malicious pages, track their activity and decide whether they should receive malware or be redirected to a scam.
MayaBot Malware Used in the Attacks
One of the campaign’s primary malware families is a custom threat called MayaBot.
Researchers said BengalSEO has been using MayaBot since at least 2022. The malware provides command-and-control capabilities, monitors infected systems and can deliver an XMRig cryptocurrency miner.
This means victims may face more than just a fraudulent webpage. A successful infection can give attackers persistent access to a compromised system and allow them to use its computing resources for cryptocurrency mining.
Fake Bitdefender Pages Used as Lures
One example identified by researchers targeted people searching for information about logging into Bitdefender Central.
A search for “bitdefender central how to login” could lead users to a fraudulent page hosted on Read the Docs infrastructure.
The page displays a prominent “Get Started” button. Clicking it begins a series of redirects through attacker-controlled domains.
During the redirection process, the infrastructure fingerprints the visitor’s browser and determines which landing page or payload should ultimately be displayed.
In some cases, victims are directed toward malware. In others, they are sent to fraudulent technical support pages designed to convince them to call a scam call center.
Black-Hat SEO Techniques Drive Traffic
BengalSEO relies heavily on search-engine manipulation to bring victims to its malicious pages.
Researchers identified several techniques used by the operation, including:
- Keyword stuffing
- Backlink manipulation
- DOM injection
- DOM shuffling
- Large-scale user-generated-content spam
The attackers reportedly flood forums and comment sections with links to malicious lure pages in an effort to generate backlinks.
For example, researchers identified pages such as viziocomsetupentercode.github[.]io, which claimed to provide instructions for setting up Vizio smart TVs.
That particular page had approximately 2,000 backlinks from 167 unique external domains, illustrating the scale of the link-building operation.
The objective is to artificially increase the authority and visibility of malicious pages so they appear higher in search results.
DOM Shuffling Helps Evade Detection
Another technique used by BengalSEO is known as DOM shuffling.
The technique dynamically rearranges HTML elements using JavaScript, changing the structure of a webpage without necessarily changing its visible content.
This allows attackers to deploy essentially identical setup guides across hundreds of domains while making them appear different to search-engine crawlers and automated security systems.
The approach can make it harder for detection mechanisms to identify large numbers of pages as duplicates or parts of the same campaign.
Traffic Distribution System Filters Victims
Before visitors reach the final payload or scam page, BengalSEO’s infrastructure uses a traffic distribution system to determine whether a visitor should proceed.
The system can act as a gatekeeper, filtering out security researchers, automated scanners, crawlers and bots.
Some redirector domains display Cloudflare Turnstile or hCaptcha challenges before continuing the attack chain.
The campaign also uses analytics technology to track and fingerprint visitors.
Researchers found Matomo tracking scripts embedded in lure and landing pages. The information is sent to a domain associated with the campaign, allowing operators to collect information about visitors.
Other hosting platforms, including GitHub Pages and Cloudflare Pages, were found using services such as Google Tag Manager for analytics and tracking.
Fake Downloads Deliver JavaScript Malware
Once a victim passes through the redirection system, they may reach a page that appears to offer legitimate software.
A typical page contains a “Download for Windows” button. Clicking the button downloads a ZIP archive containing a JavaScript-based dropper disguised as the advertised application.
The script is executed through wscript.exe, launching the MayaBot infection chain.
In some cases, however, no malware is delivered.
Instead, victims are redirected to a fraudulent support page warning them about supposed suspicious activity associated with an account such as Bitdefender Central.
The page then instructs the victim to call a telephone number operated by BengalSEO’s scam call center.
Trusted Hosting Platforms Abuse Their Reputation
BengalSEO has also taken advantage of legitimate hosting platforms, including:
- GitHub Pages
- Cloudflare Pages
- Google Sites
- Read the Docs
Using these services can help malicious pages benefit from the reputation and trust associated with well-known domains.
The campaign’s GitHub infrastructure is particularly extensive.
The DFIR Report identified as many as 84 active BengalSEO-linked GitHub accounts between January 2024 and March 2026.
Researchers examined commit histories and found email addresses connecting some of these accounts to Garage2Global-related domains.
The malicious pages are also regularly modified. Attackers can use new commits to replace blocked redirector domains, rotate infrastructure or temporarily substitute legitimate URLs.
This allows the operation to adapt quickly when domains are detected and removed.
Large Infrastructure Network
Much of BengalSEO’s infrastructure was registered from August 2025 onward, with activity increasing throughout late 2025 and into early 2026.
Researchers said the campaign has registered domains across several top-level domains, including .my, .shop and .info.
Between 2023 and 2026, the group reportedly registered domains primarily through Spaceship and Namecheap.
For hosting and traffic proxying, the attackers heavily relied on Cloudflare, which accounted for more than 80% of the domains observed by researchers. Hostmaza was identified as the origin host for another portion of the infrastructure.
One account associated with redirector domains was reportedly suspended by Hostmaza earlier this year.
Another SEO Campaign Targets Trusted Websites
The BengalSEO disclosure comes as Check Point Research has reported a separate SEO manipulation campaign targeting websites belonging to Brazilian government and educational organizations.
The activity has been linked to a Chinese-speaking cybercrime cluster known as Gambling Goblin, which researchers associate with the threat actor Earth Berberoka, also known as GamblingPuppet.
Unlike BengalSEO, this campaign reportedly compromises legitimate websites and uses them as infrastructure for SEO manipulation and phishing.
Researchers said the campaign has been active since at least mid-2025.
Attackers Turn Legitimate Websites Into Phishing Infrastructure
According to Check Point, attackers install malicious Apache modules on compromised servers.
These modules can secretly reverse-proxy visitors to attacker-controlled phishing pages while making the traffic appear to originate from the legitimate website.
The attackers also remove the site’s existing Content Security Policy (CSP) headers, allowing injected content to operate without being blocked by the browser’s security controls.
Once attackers gain access, they can deploy a Linux-based toolkit containing several components, including:
- A Go-based downloader known as DownPro
- Backdoors including AlphaAgent, ChUser and oRAT
- A password-stealing tool
- An SSH brute-forcing component
- A reconnaissance agent
- Malicious Apache modules used to proxy visitors
The exact method used to initially compromise the websites remains unknown.
Phishing Pages Impersonate Major App Stores
The compromised websites are then used to host or redirect visitors to phishing pages that imitate trusted platforms such as Google Play, Microsoft Store and Amazon.
The attackers use the reputation of legitimate government, education and other trusted domains to improve search rankings and redirect users toward online gambling and sports-betting content.
However, researchers warn that the same infrastructure could potentially be adapted to deliver malware.
By compromising highly trusted websites and presenting fake software-download pages, attackers could potentially place malicious downloads directly in front of users who believe they are interacting with a legitimate service.
SEO Poisoning Remains a Serious Threat
The BengalSEO campaign highlights how search engines can become an entry point for malware and fraud.
Rather than relying exclusively on phishing emails or malicious advertisements, attackers can manipulate search results so that victims themselves navigate to fraudulent websites while looking for legitimate information.
The combination of black-hat SEO, large-scale backlink spam, trusted hosting services, browser fingerprinting and sophisticated traffic filtering makes campaigns such as BengalSEO difficult to disrupt.
For users, the safest approach is to avoid downloading software or calling support numbers found through unexpected search results. When looking for account support, software downloads or service activation instructions, users should navigate directly to the official website rather than relying on unfamiliar search results.
For organizations, monitoring for unexpected changes to website content, suspicious redirects, unauthorized Apache modules and unusual outbound connections can help identify potential compromise before attackers can turn trusted websites into tools for SEO poisoning and malware distribution.
