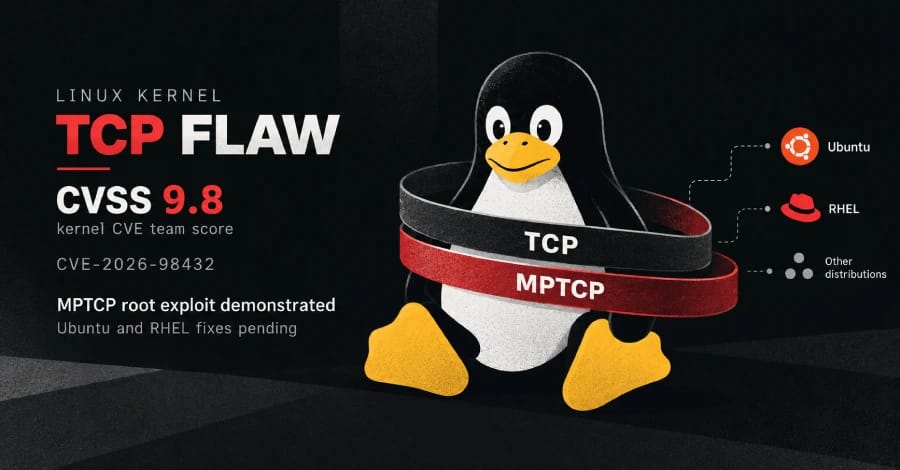
A critical security vulnerability in the Linux kernel’s TCP implementation could allow remote attackers to execute arbitrary commands with root privileges on vulnerable Linux servers. Tracked as CVE-2026-98432, the flaw has received a maximum-severity CVSS score of 9.8 from the Linux kernel’s CVE team.
The vulnerability affects multiple Linux distributions, including Ubuntu and Red Hat Enterprise Linux (RHEL). However, as of October 29, 2026, neither Ubuntu nor Red Hat has released a patched kernel for the affected versions.
Anthropic disclosed on October 27 that its artificial intelligence model, Claude, successfully developed an exploit for the vulnerability. The exploit reportedly allows an unauthenticated remote attacker to gain root-level access to Linux servers running a Multipath TCP (MPTCP) listener.
Interestingly, security vendors have assigned different severity ratings to the vulnerability. Red Hat, Amazon, Oracle, and SUSE have rated it between 5.9 and 8.1, considerably lower than the Linux kernel team’s 9.8 assessment.
Linux Kernel Vulnerability CVE-2026-98432 Explained
The security issue originates from a race condition in the Linux kernel’s TCP connection-handling code, specifically during the establishment of new IPv4 TCP connections.
The flaw can trigger a use-after-free vulnerability, a type of memory safety issue that occurs when software attempts to access memory that has already been released.
Under certain conditions, the kernel may continue accessing previously freed memory while processing a new or retransmitted TCP connection request. This could potentially allow an attacker to leak sensitive kernel memory, corrupt memory, or crash the affected system.
The vulnerability was introduced in Linux kernel version 4.4. Kernel developers addressed the issue on October 5, 2026, ten days before the CVE was publicly disclosed.
The fix ensures that the kernel waits until other CPUs have finished accessing the relevant IP options before releasing the associated memory.
Notably, IPv6 connections are not affected by this particular race condition because the kernel copies the IP options when establishing IPv6 connections.
Which Linux Distributions Are Affected?
CVE-2026-98432 impacts several Linux distributions, although the availability of security updates varies between vendors.
As of October 29, 2026, Debian, Oracle Linux, SUSE Linux Micro, openSUSE Leap, and certain Amazon Linux kernel packages have received fixes. Ubuntu and RHEL users are still waiting for updated kernel packages.
The following table summarizes the reported vulnerability status and available fixes.
Linux Distribution Patch Status
| Linux Distribution | Vendor Severity | Status as of October 29 | Fixed Package or Advisory |
|---|---|---|---|
| Ubuntu 22.04, 24.04, 26.04 and 26.10 | High | Work in progress | No fix released |
| Ubuntu 16.04, 18.04 and 20.04 | High | Vulnerable | No fix released |
| RHEL 8, 9, 10 and OpenShift 4 | Moderate (5.9) / Important (8.1) | Fix deferred | No fix released |
| RHEL 7 | Not applicable | Not affected | Not required |
| Amazon Linux 2023 (kernel 6.18) | Important (7.0) | Fixed October 24 | kernel6.18-6.18.56-125.164.amzn2023 |
| Amazon Linux 2023 (kernel 6.12) | Important (7.0) | Fixed October 29 | kernel6.12-6.12.113-138.209.amzn2023 |
| Amazon Linux 2 | Important (7.0) | Pending | No fix released |
| Oracle Linux 7, 8, 9 and 10 | Important (8.1) | Fixed October 16 | ELSA-2026-500397, ELSA-2026-500398, ELSA-2026-500399 |
| Debian 13 (Trixie) | No score listed | Fixed October 16 | linux 6.12.113-1 |
| Debian 12 (Bookworm) | No score listed | Fixed October 17 and 22 | linux 6.1.190-1; linux-6.12 6.12.113-1~deb12u1 |
| SUSE Linux Micro 6.2 and openSUSE Leap 16.0 | Important (8.1) | Fixed | kernel-default 6.12.0-160000.40.1 or later |
| SLES 15 SP4–SP6 LTSS, SLES 16.0 and SLE Micro 5.3–5.5 | Important (8.1) | In testing | No fix released |
| SLES 15 SP7 | Important (8.1) | Fix in progress | No fix released |
Ubuntu has also listed its cloud, FIPS, and real-time kernel variants as vulnerable or under investigation.
Red Hat has confirmed that fixes for affected products are currently deferred to a future update. Neither Red Hat nor Ubuntu has provided a confirmed release date.
Amazon Linux users should also note that the vendor’s CVE page and security advisory did not show identical statuses for the kernel 6.12 package as of October 29.
How the Linux Kernel Race Condition Works
The vulnerability occurs during the TCP three-way handshake, when the Linux kernel processes incoming connection requests.
When a new IPv4 TCP connection is completed, the kernel transfers IP options associated with the pending connection request to the newly created socket without copying them.
A race condition can occur if the socket is destroyed while another CPU is still accessing those IP options to process a retransmitted connection request.
As a result, the kernel may attempt to read memory that has already been freed.
This use-after-free condition creates an opportunity for an attacker to manipulate kernel memory and potentially compromise the system.
The vulnerability affects IPv4 connections, while IPv6 connections are protected from this specific issue because their IP options are copied rather than transferred in the same manner.
Why Security Vendors Assigned Different CVSS Scores
One of the notable aspects of CVE-2026-98432 is the significant difference between the severity ratings assigned by the Linux kernel team and individual Linux vendors.
On October 24, the Linux kernel’s CVE team assigned the vulnerability a CVSS score of 9.8, placing it in the critical severity category.
The assessment assumes that an attacker can send a TCP connection request containing IPv4 Record Route or Timestamp options and subsequently retransmit the request to trigger the race condition.
The kernel team classified the attack complexity as low, arguing that the attacker can deliberately influence both sides of the race.
Successful exploitation could potentially expose nearby kernel memory, corrupt kernel memory, or cause a system crash.
However, Red Hat assigned a lower score of 5.9 on its CVE page, classifying the vulnerability as Moderate. The company considers winning the race condition difficult and identifies a kernel crash as the most likely consequence.
Red Hat also noted that memory corruption is theoretically possible but that no confidentiality or integrity impact had been demonstrated.
Interestingly, Red Hat’s machine-readable security advisory, updated on October 29, classified the issue as Important and assigned a CVSS score of 8.1. Its bug tracker also changed the vulnerability’s severity from medium to high on the same day.
Oracle and SUSE have similarly assigned a score of 8.1, while Amazon rated it 7.0.
The differences primarily stem from how vendors assess attack complexity and the likelihood of successfully exploiting the race condition.
As of October 28, the National Vulnerability Database (NVD) had not published an independent CVSS assessment and displayed the Linux kernel team’s 9.8 score.
Anthropic’s Claude AI Developed a Working Linux Exploit
On October 27, Anthropic published details about several security vulnerabilities that its AI model, Claude, had successfully identified and exploited.
One of the examples involved CVE-2026-98432, where Claude reportedly developed a working exploit following initial prompting.
According to Anthropic, the exploit operates in two stages.
Stage 1: Kernel Address Disclosure
The attacker first exploits the race condition to make the Linux kernel return additional bytes of memory to the remote system.
If one of these responses contains a kernel memory address, the attacker can use the information to bypass Kernel Address Space Layout Randomization (KASLR).
KASLR is a security mechanism designed to make exploitation more difficult by randomizing the locations of kernel memory structures.
Stage 2: Remote Root Command Execution
After obtaining a kernel memory address, the exploit uses the same vulnerability to trigger a buffer overflow.
The attacker overwrites a callback pointer with the address of a payload previously placed in kernel memory.
When the kernel subsequently executes the modified callback pointer, the attacker’s payload runs a shell command with root privileges.
Anthropic reported that an unsuccessful race attempt only affects the individual connection attempt rather than crashing the system. This allows an attacker to repeat the process until exploitation succeeds.
During its testing, the company reported that obtaining a kernel memory address took approximately 48 minutes, while achieving command execution required another five minutes.
However, Anthropic did not publish the exploit code, the exact Linux kernel version used in its testing, or the specific system configuration.
Multipath TCP Plays a Key Role in the Exploit
Anthropic’s research specifically describes exploitation against Linux servers running a Multipath TCP listener.
Multipath TCP, commonly known as MPTCP, is a TCP extension that allows a single connection to use multiple network paths simultaneously.
On Linux systems, applications must explicitly request MPTCP functionality when creating a socket.
Red Hat has warned that a remote attacker capable of reaching an exposed TCP service could potentially trigger the race condition.
However, Anthropic’s published exploit targeted systems with an MPTCP listener. Its research does not establish whether servers without this feature can be compromised using the same root-level exploit technique.
Neither the original CVE record nor the kernel patch explicitly mentions MPTCP. The connection between the vulnerability and this particular networking feature comes from Anthropic’s exploitation research.
No Evidence of Active Attacks Reported So Far
Despite the critical severity rating and Anthropic’s demonstration of remote root command execution, there were no publicly reported incidents of attackers exploiting CVE-2026-98432 in the wild as of October 29, 2026.
The vulnerability was also absent from the available copy of CISA’s Known Exploited Vulnerabilities (KEV) catalog last updated by Luxembourg’s CIRCL on October 28.
Nevertheless, the ability to achieve unauthenticated remote root access makes the vulnerability a significant security concern for organizations operating exposed Linux infrastructure.
How to Protect Linux Systems Against CVE-2026-98432
Linux administrators should prioritize installing the appropriate security updates as soon as they become available for their distributions.
Organizations using distributions that have already released patched kernel packages should apply the updates and reboot affected systems where necessary.
For administrators building custom Linux kernels, the vulnerability has been fixed in the following stable kernel releases:
- Linux 5.10.272
- Linux 5.15.223
- Linux 6.1.190
- Linux 6.6.159
- Linux 6.12.113
- Linux 6.18.56
- Linux 7.2.10
- Linux 7.3
The Linux kernel’s CVE team recommends upgrading to the latest stable kernel rather than selectively applying individual patches. The kernel community does not officially support cherry-picking isolated fixes.
Organizations running Ubuntu, RHEL, and certain Amazon Linux and SUSE versions should continue monitoring their respective vendor security advisories for updated kernel packages.
Red Hat has stated that no currently available mitigation meets its requirements for broad applicability, deployment simplicity, and stability. Other vendor advisories have also not identified a confirmed workaround.
Additionally, neither Anthropic’s research nor the available vendor advisories establish whether disabling Multipath TCP or blocking incoming TCP connection requests containing IP options would sufficiently reduce the exploitation risk.
Until official fixes become available, administrators should maintain close monitoring of vendor advisories, assess exposure across internet-facing Linux servers, and prioritize patch deployment once supported updates are released.
Bottom Line: CVE-2026-98432 highlights the growing security risks associated with memory safety vulnerabilities in critical operating system components. Anthropic’s demonstration that an AI model could develop an exploit capable of achieving remote root access further underscores the importance of timely kernel security updates and proactive vulnerability management.
