A growing Android banking trojan called RatHat is being operated through a web-based control panel that uses Google’s Gemini AI to help attackers identify potentially valuable victims, according to cybersecurity company Cleafy.
Cleafy said it has identified nearly 100 deployments of the RatHat control console since April 2026, indicating that the malware is being offered through a malware-as-a-service (MaaS) model. Under this model, different customers can operate their own copy of the infrastructure.
The web console allows operators to manage infected Android devices and view information collected from victims, including text messages and credentials entered into fake login screens displayed over legitimate banking applications.
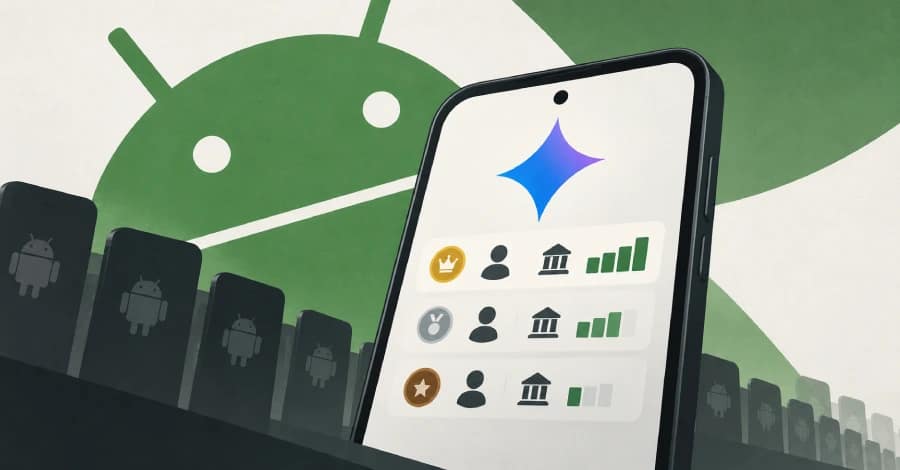
The latest version adds an unusual feature: it uses Google’s Gemini AI model to estimate a victim’s bank balance based on intercepted messages and then categorizes infected devices into high-value and mid-value groups.
Cleafy said it found no evidence that Gemini is being used to directly transfer money. Instead, the AI appears to help criminals determine which victims are worth targeting further.
RatHat’s Control Console Has Evolved
While the malware installed on Android devices has changed relatively little since late 2025, the infrastructure used to control it has undergone several updates.
Earlier samples identified by Cleafy in late 2025 and February 2026 connected to a control panel called Fisher.
Between April and September 2026, researchers identified three newer versions based on the same underlying code:
- BlackCat Remote Control Management
- Panda Workshop V5
- Panda Workshop V6
The control panels serve as more than simple command-and-control systems. They also function as malware-building platforms.
Operators can use the console to generate a RatHat build, disguise it inside an apparently legitimate application and sign the resulting APK. The finished application can then be published directly to services such as Amazon S3 or a web server without requiring the operator to configure the hosting infrastructure manually.
The console can also automatically rebuild the malware at scheduled intervals, including as frequently as once an hour.
Each rebuild produces a new file even though the underlying malware remains the same. According to Cleafy, this feature appears designed to make detection more difficult for security products that identify malicious files using their hashes.
The latest console also includes templates for fake application download pages, including one labeled Google Store.
RatHat Can Gain Shell Access With One Click
RatHat can reach Android devices through SMS messages and online advertisements that direct users to third-party download websites, according to research previously published by Zimperium.
After installation, the malware requests Android Accessibility access. This powerful permission allows applications to read information displayed on the screen and interact with the device on behalf of the user.
RatHat uses that access to enable wireless debugging, retrieve the pairing code displayed on the device and connect to Android Debug Bridge (ADB), Google’s built-in Android debugging system.
The process gives the malware access to a shell running as Android’s shell user, UID 2000, operating outside the normal permissions assigned to the malicious application.
Cleafy found that operators can access this shell directly from the control panel using a single deployment button.
Clicking the button launches a separate program written in Go, which establishes a reverse tunnel between the infected phone and the attacker’s infrastructure.
The ADB pairing process can occur automatically, but the Go component is launched only when the operator chooses to deploy it.
Stealthier Screen Monitoring
RatHat provides multiple ways for attackers to monitor and interact with infected devices.
The malware’s built-in screen-capture capability relies on an Android feature that normally requires user authorization. When active, Android displays a recording indicator to the victim.
The Go-based component takes a different approach.
It uses two tools known as minicap and minitouch to stream the device’s screen and simulate touch input. According to Cleafy, this method can operate without displaying the standard permission prompt or recording indicator.
However, the technique has a significant limitation: minicap and minitouch do not work on Android 14 and later.
On newer Android versions, RatHat falls back to its own screen-capture mechanism, which requires the normal Android permission and displays the corresponding indicator.
Cleafy also identified another fallback based on the Android screencap tool, operating at approximately five frames per second. The researchers did not specify which Android versions are supported by that method.
Malware Can Survive App Removal
The Go component can remain active even after the victim removes the RatHat application.
According to Cleafy, the component continues running until the device is restarted.
Zimperium also found that the malware can potentially reinstall the application after it has been removed and restore its Accessibility access.
Neither Cleafy nor Zimperium provided instructions for completely removing the malware from an infected device.
Nearly 100 RatHat Console Deployments Identified
Cleafy discovered the RatHat infrastructure by searching for distinctive control-panel page titles and web code.
The company said it identified nearly 100 console deployments since April 2026.
However, that figure does not represent the number of infected phones or victims.
Cleafy did not specify precisely what constitutes a single deployment, and the available research does not provide a reliable estimate of the number of infected devices.
The console limits the number of operator accounts and restricts access to certain sections for non-administrators. Cleafy said those controls suggest that the developers may not fully trust the customers using the infrastructure.
Researchers also found that almost half of the observed IP addresses were associated with a Singapore-registered network identified as AS4907.
Gemini AI Used to Rank Potential Victims
Artificial intelligence has become an unusual part of RatHat’s operation.
Earlier versions of the control panel allowed operators to select from multiple AI providers. The system could also send Telegram notifications when an infected device received an AI score above a specified threshold.
The latest version has switched exclusively to Google Gemini and directs operators to Google AI Studio to obtain an API key.
The AI is used to analyze information stolen from victims, including messages that could reveal financial information.
Cleafy found that the system can use Gemini to estimate the victim’s bank balance and categorize devices according to their potential value.
The apparent purpose is prioritization rather than automated theft.
In other words, the AI helps attackers decide which infected devices deserve more attention.
RatHat Also Uses Gemini on Android Devices
Gemini is not limited to the attacker’s control panel.
RatHat also uses Google’s AI model directly on infected Android devices.
The malware contains predefined instructions for interacting with specific combinations of smartphone manufacturers, Android versions and languages. These instructions can fail when RatHat encounters a device configuration that its developers did not anticipate.
When that happens, the malware can send the device’s screen layout to Gemini and ask the AI to determine where the attacker should tap.
The request is sent directly from the infected device using an API key stored in the malware’s configuration.
Cleafy said this AI capability is currently used to help the malware complete the wireless debugging setup, rather than to conduct financial transactions.
The technique is not entirely new. ESET described another Android threat called PromptSpy in February that similarly sent screen layouts to Gemini and followed the model’s instructions for interacting with the device.
RatHat Indicators of Compromise
Cleafy published several indicators associated with RatHat’s command-and-control infrastructure, download sites and malware samples.
Among the indicators are:
- Panda Workshop V6 C2:
admin.chunhuating[.]best - Panda Workshop V5 C2:
admin.xiongmaocs[.]pics - BlackCat C2:
8.231.120[.]246 - Fisher C2:
admin.rathat[.]live - Download URL:
hxxps://dramaspoolcoa[.]com/en.html - Earlier download URL:
hxxps://rathat[.]me/app-release-rat-hat-live.apk
Cleafy also identified several malware file hashes:
116346cace7f00ba557034b534d407918fdc21e25097a46528211274e54330e1f83357b2d47c7d38ee53943373961211
The RatHat consoles commonly use web addresses beginning with admin., while the newest version also uses adminapi. for backend services.
Researchers noted that the infrastructure frequently relies on inexpensive top-level domains such as .best, .beer and .top.
Security Teams Can Monitor for RatHat Activity
Cleafy said security products can look for the presence of the minicap and minitouch components under /data/local/tmp once the Go-based program has been deployed.
Security teams can also monitor processes running under Android’s shell user, UID 2000, which may help identify suspicious activity associated with the malware’s ADB-based capabilities.
One of the domains identified by Cleafy, admin.xiongmaocs[.]pics, also appeared in the indicators published by Zimperium in its earlier analysis.
RatHat Shows How Android Malware Is Adapting to AI
RatHat demonstrates how cybercriminals are incorporating AI into different stages of malware operations.
In this case, Gemini is being used for two distinct purposes: helping the malware interact with unfamiliar Android interfaces and helping operators prioritize potentially valuable victims.
The research does not indicate that Gemini is directly conducting unauthorized financial transactions. Instead, its apparent role is to automate tasks that previously required attackers to spend more time manually analyzing infected devices.
With RatHat’s control infrastructure increasingly packaged as a service, the combination of automated malware generation, remote device control and AI-assisted victim prioritization could make the threat more scalable for its operators.
