The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a security vulnerability affecting Broadcom VMware ESXi to its Known Exploited Vulnerabilities (KEV) catalog, following disclosures that a China-linked threat actor known as Warp Panda exploited the flaw in cyberattacks targeting organizations in the U.S. legal sector.
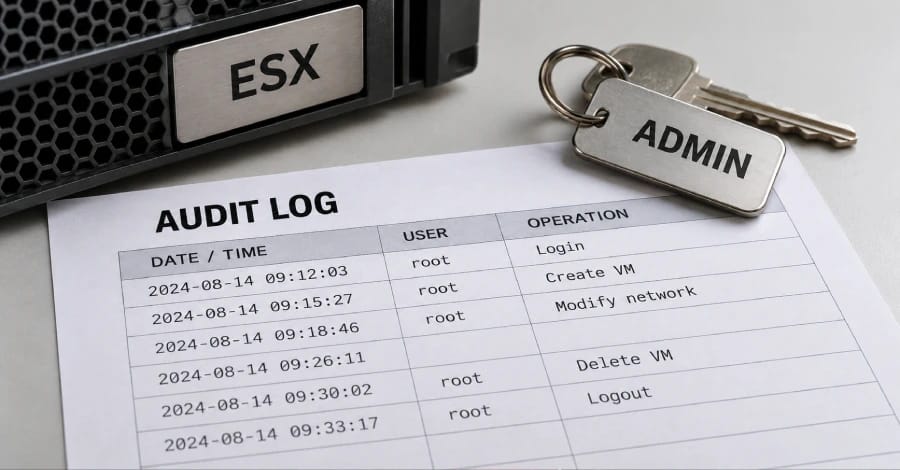
The vulnerability, tracked as CVE-2026-41709 with a CVSS score of 2.7, stems from insufficient logging in VMware ESXi. It could allow an attacker with administrative privileges to perform certain operations without generating corresponding audit log entries, potentially making malicious activities harder to detect.
VMware Releases Security Updates for CVE-2026-41709
In a security advisory published in July 2026, Broadcom confirmed that the vulnerability had been addressed in the following product versions:
- VMware Cloud Foundation: SxI-9.1.0.0-25370933 and ESXi-9.0.2.0100-25595025
- VMware vSphere Foundation: SxI-9.1.0.0-25370933 and ESXi-9.0.2.0100-25595025
- VMware ESX: ESXi80U3j-25429389
- VMware Cloud Foundation 5.2.4
- VMware Telco Cloud Platform: ESXi80U3j-25429389
Organizations running affected VMware environments are advised to review Broadcom’s security advisory and install the applicable updates.
Warp Panda Exploited VMware Flaw as a Zero-Day
The development follows findings published in CrowdStrike’s 2026 Legal Threat Landscape Report, which revealed that Warp Panda exploited CVE-2026-41709 as a zero-day vulnerability in early 2026.
According to CrowdStrike, the attackers leveraged the flaw to reduce audit trail visibility and conceal their activities within compromised environments.
“Warp Panda exploits internet-facing edge devices using zero-day vulnerabilities and custom malware to maintain covert, persistent access,” CrowdStrike noted in its report shared with The Hacker News.
The threat actor also reportedly bypasses security monitoring mechanisms by disabling or circumventing audit logging, stealing cloud session tokens, and registering unauthorized multi-factor authentication (MFA) devices.
Warp Panda’s History of Zero-Day Exploitation
Also tracked as Armory Castle (formerly UNC5221), Clay Typhoon, and VerdantBamboo, Warp Panda has a history of exploiting zero-day vulnerabilities in enterprise-facing technologies, including Citrix NetScaler and Ivanti Connect Secure appliances.
Earlier this month, Google-owned Mandiant attributed the exploitation of a critical improper origin validation vulnerability in BeyondTrust Remote Support (CVE-2026-102764, CVSS score: 9.3) to the hacking group.
The attackers reportedly exploited the flaw to deploy custom malware families, including SAWFLY and BARECLAW.
How Warp Panda Conducts Its Cyberattacks
Warp Panda’s attack operations typically begin by compromising internet-facing edge devices through previously unknown vulnerabilities. Following initial access, the attackers move laterally into VMware vCenter environments and deploy custom malware to establish persistent access.
Some of the malware families associated with these operations include:
- BRICKSTORM: A custom backdoor used to maintain persistent access within compromised environments.
- SharpStorm: Another malware tool leveraged by the threat actor to support covert operations.
The group’s activities also extend to cloud environments, where attackers attempt to steal user session tokens to gain access to Microsoft 365 accounts without triggering conventional credential-based security alerts.
In at least one documented incident, Warp Panda reportedly registered a new MFA device on a compromised account. This allowed the attackers to maintain access even after the account’s password was changed.
U.S. Legal Sector Remains a High-Value Target
CrowdStrike describes Warp Panda as a persistent and strategically focused China-linked cyber espionage threat targeting U.S. organizations across multiple industries, including the legal sector.
The legal industry is particularly attractive to state-sponsored threat actors because law firms and legal service providers hold sensitive information, including confidential client communications, merger and acquisition documents, litigation strategies, and information spanning multiple clients.
Access to such data could provide valuable intelligence with potential operational and strategic implications.
CISA Sets November 11, 2026, Deadline for Federal Agencies
Following the confirmation of active exploitation, CISA added CVE-2026-41709 to its Known Exploited Vulnerabilities catalog.
Under Binding Operational Directive (BOD) 22-01, Federal Civilian Executive Branch (FCEB) agencies are required to address vulnerabilities included in the KEV catalog within the specified remediation timeframe.
For CVE-2026-41709, affected federal agencies have been directed to apply the necessary security updates by November 11, 2026.
Although the vulnerability carries a relatively low CVSS score of 2.7, its exploitation by a sophisticated China-linked threat actor highlights the importance of addressing weaknesses that could undermine security monitoring and forensic visibility.
Organizations using affected VMware products should prioritize patch deployment, review administrative activity logs, investigate suspicious operations, and strengthen monitoring across VMware and connected cloud environments.
